New Malicious Campaign Targets Atomic and Exodus Wallets
The security firm ReversingLabs’ research team has discovered yet another campaign targeting specific versions of the popular crypto wallets Exodus and Atomic.According to the report, threat actors “have been targeting t...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
The security firm ReversingLabs’ research team has discovered yet another campaign targeting specific versions of the popular crypto wallets Exodus and Atomic.
According to the report, threat actors “have been targeting the cryptocurrency community hard lately.” They’re using various methods to hijack popular and legitimate crypto packages to loot people’s wallets.
However, the researchers highlight that hijacking open-source packages is difficult due to the size of the open-source software (OSS) developer community. The tampered-with OSS packages will be detected.
RL researchers have identified yet another #npm package that uses malicious patching of local software to hijack #cryptocurrency transfers. Get the full story. https://t.co/lbyNR5cp8Z
— ReversingLabs (@ReversingLabs) April 10, 2025Therefore, threat actors are working hard to make their methods more obscure. A new technique that ReversingLabs discovered is uploading packages to OSS repositories and having them apply malicious ‘patches’ to local versions of legitimate libraries.
The goal is the same: install an unnoticeable malicious code in a popular, trusted local library.
The researchers found “a number of campaigns” in recent weeks attempting this strategy. Notably, on 1 April, a malicious entity published a package, pdf-to-office, to the npm package manager. This package posed as a library for converting PDF to Microsoft Office documents.
Once executed, it would inject malicious code into locally installed Atomic Wallet and Exodus. It would overwrite existing files. “Effectively, a victim who tried to send crypto funds to another wallet would have the intended destination address swapped out for one belonging to the malicious actor,” the report states.
List of TH policies in package [email protected]. Source: ReversingLabsAdditionally, this campaign is quite similar to the one the researchers discussed in a research post in March.
In both of these cases, the malicious campaign had no effect on the official Atomic Wallet and Exodus Wallet installers available on the websites.
You might also like N.Korean Hackers Boost Crypto-Looting Methods: Hiding Malware in GitHub, NPM Packages Aiming for Specific Wallet VersionsReversingLabs first detected the pdf-to-office package after its update to npm on 1 April. It was removed soon after detection. But a couple of days later, the threat actor published a new version that looked like the first one. They released three versions of the package over a few weeks in March and April with the same functionality.
The malicious payload worked to detect the presence of the atomic/resources/app.asar archive inside AppData/Local/Programs directory. Finding it would mean that the unsuspecting user installed Atomic Wallet on their now-infected computer.
Then, the malicious code searched for the archive to overwrite one of its files with a trojanized version that changes the outgoing crypto address. Now, the funds would go straight to the threat actor’s wallet.
“That was the only difference between the legitimate and trojanized file, except that the malicious version of the file was not minified,” the report notes.
The difference between a legitimate and trojanized file. Source: ReversingLabsAdditionally, the threat actors focused on specific versions of Atomic. The attack code would adjust which files were overwritten based on the wallet version it found.
Moreover, there was a malicious payload that attempted to inject a trojanized file inside a legitimate, locally-installed Exodus wallet. It targeted the two latest versions of Exodus.
Also, if the victim removed the package pdf-to-office from the computer, the Web3 wallets’ software would still remain compromised. This means it would continue directing crypto to the attackers’ wallet.
“The only way to completely remove the malicious trojanized files from the Web3 wallets’ software would be to remove them completely from the computer and re-install them,” ReversingLabs concludes.
Meanwhile, North Korea’s Lazarus group has been targeting crypto developers via npm supply chain attacks for months in a highly sophisticated global campaign to steal funds and data.
You might also like Crypto Mining Malware and Open Source Malware Packages Doubled in Q1 2025The post New Malicious Campaign Targets Atomic and Exodus Wallets appeared first on Cryptonews.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
Fake AI crypto software is secretly replacing browser wallet extensions
HP Wolf Security, the company's threat-research team, said a fake AI crypto-trading assistant distributed malware that could repla...
BitGo rolls out quantum-risk management tools to shield institutional Bitcoin wallets
BitGo's quantum-risk tools enhance Bitcoin security, potentially setting a new standard for institutional crypto custody amid evol...
WaterPlum infects 30,000 devices, steals data from 7,000 crypto wallets
The WaterPlum incident underscores the growing sophistication of state-sponsored cyber threats, highlighting vulnerabilities in gl...
Your crypto hardware wallet can stay secure while everything around it fails
Two wallet incidents this week exposed a growing weakness in crypto self-custody: the systems surrounding hardware devices. D’CENT...
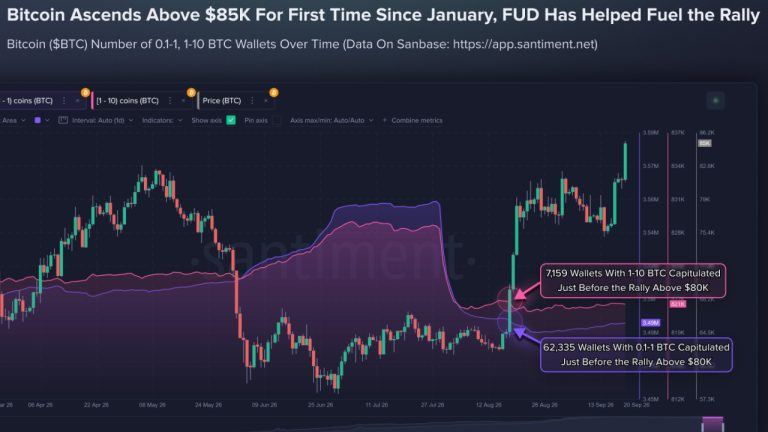
Smaller Bitcoin Holders Sold Before $85K Rally as 69,494 Wallets Exit
Bitcoin climbed above $85,000 after 69,494 wallets disappeared from two smaller-holder balance groups during the July-August downt...
SparkLend absorbs 88,320 ETH from tracked whale wallets as big money bets on conservative DeFi
Whale investments in SparkLend highlight a shift towards safer DeFi options, potentially influencing future risk management and pl...